Windows Active Directory Threat Detection Lab
(In Progress)
September 2026
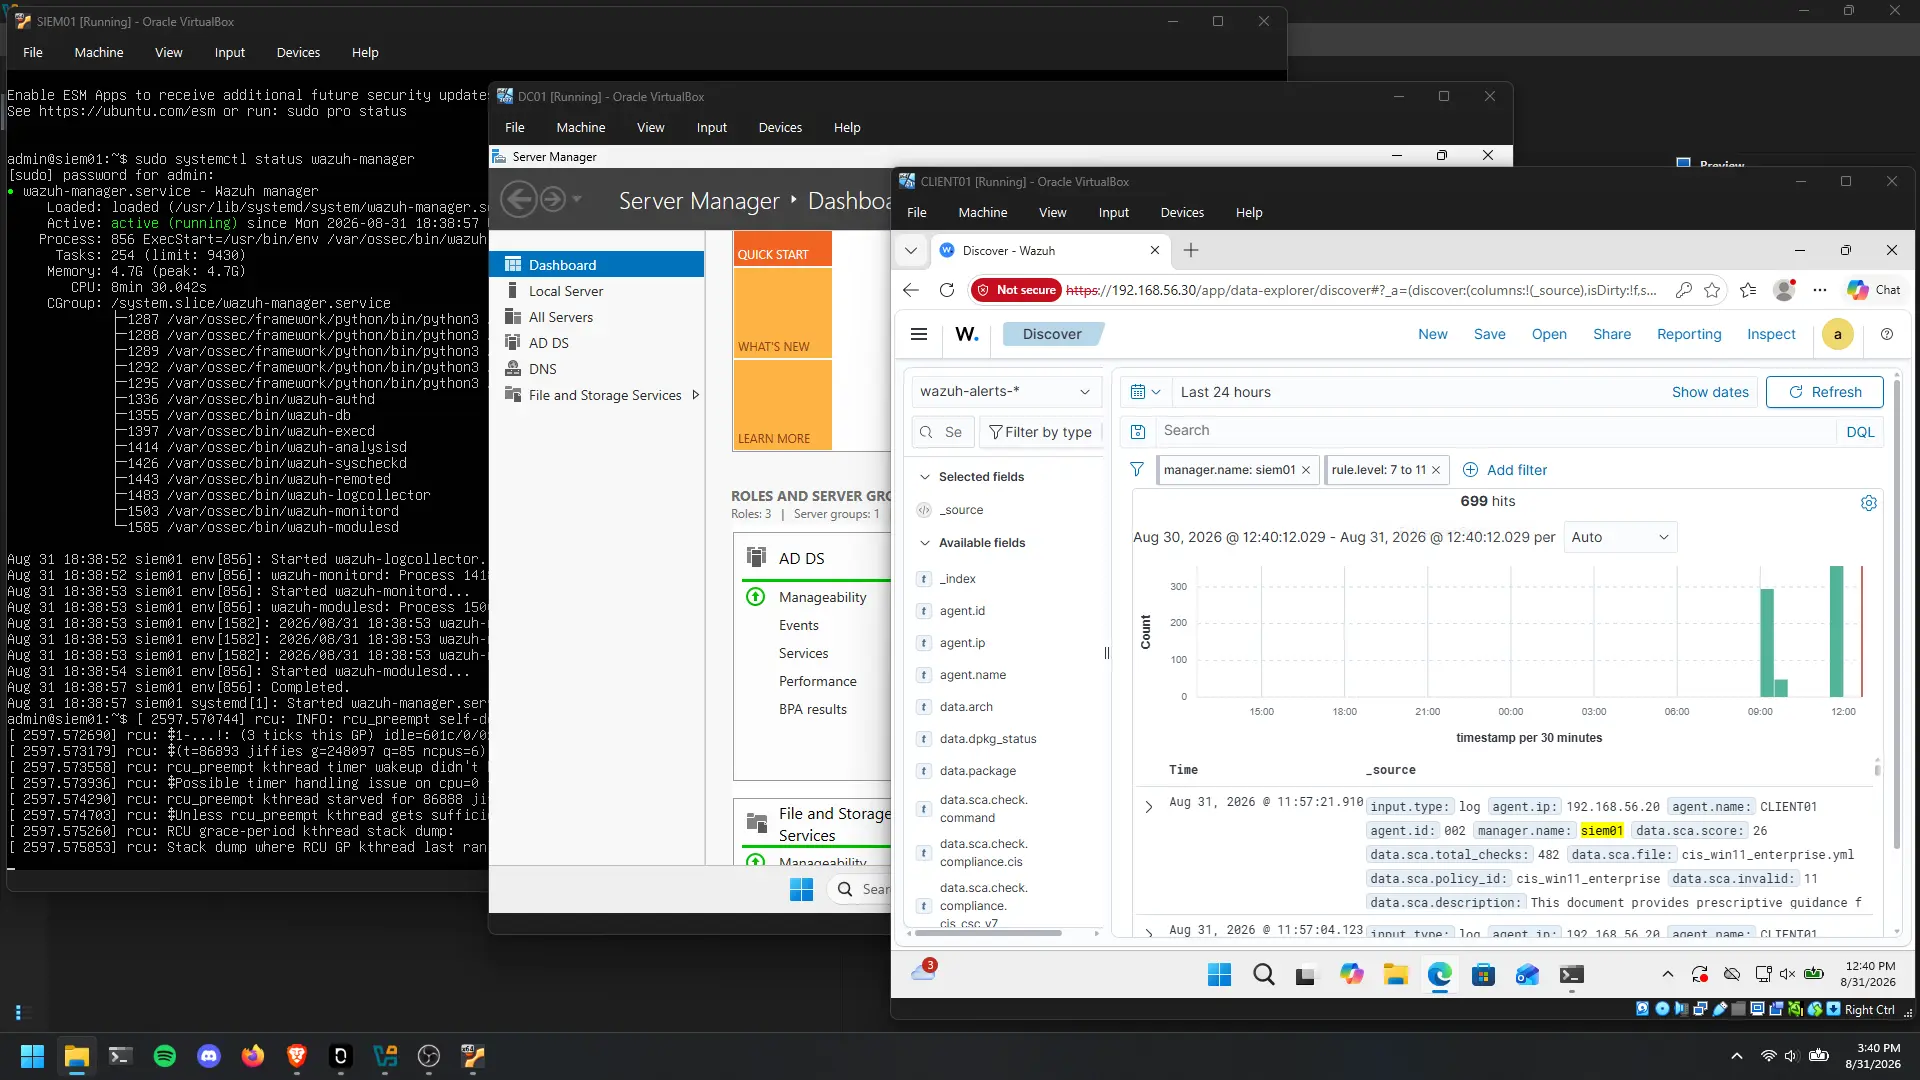
Building an Active Directory environment with a Windows Server domain controller, a domain-joined Windows 11 client, and an Ubuntu-based Wazuh SIEM to simulate real-world attack techniques in a controlled lab. Using Nmap, Hydra, and PowerShell, carried out network reconnaissance, an RDP brute-force attack against a domain account, and execution of an encoded PowerShell payload, then used Wazuh to collect and analyze the resulting logs.